Antra
Security linter that catches data leaking across trust boundaries in Next.js
Project Overview
About This Project
Antra is a static analysis security linter for React Server Components and the Next.js App Router. It finds the exact point where a value crosses a trust boundary without validation, using a schema snapshot of your data layer so it knows which fields are sensitive. Published on npm as @ferhattahar/antra-next.
The Challenge
In Next.js, data moves from the server to the browser in many places, and one unchecked value is enough to leak something private.
The Result
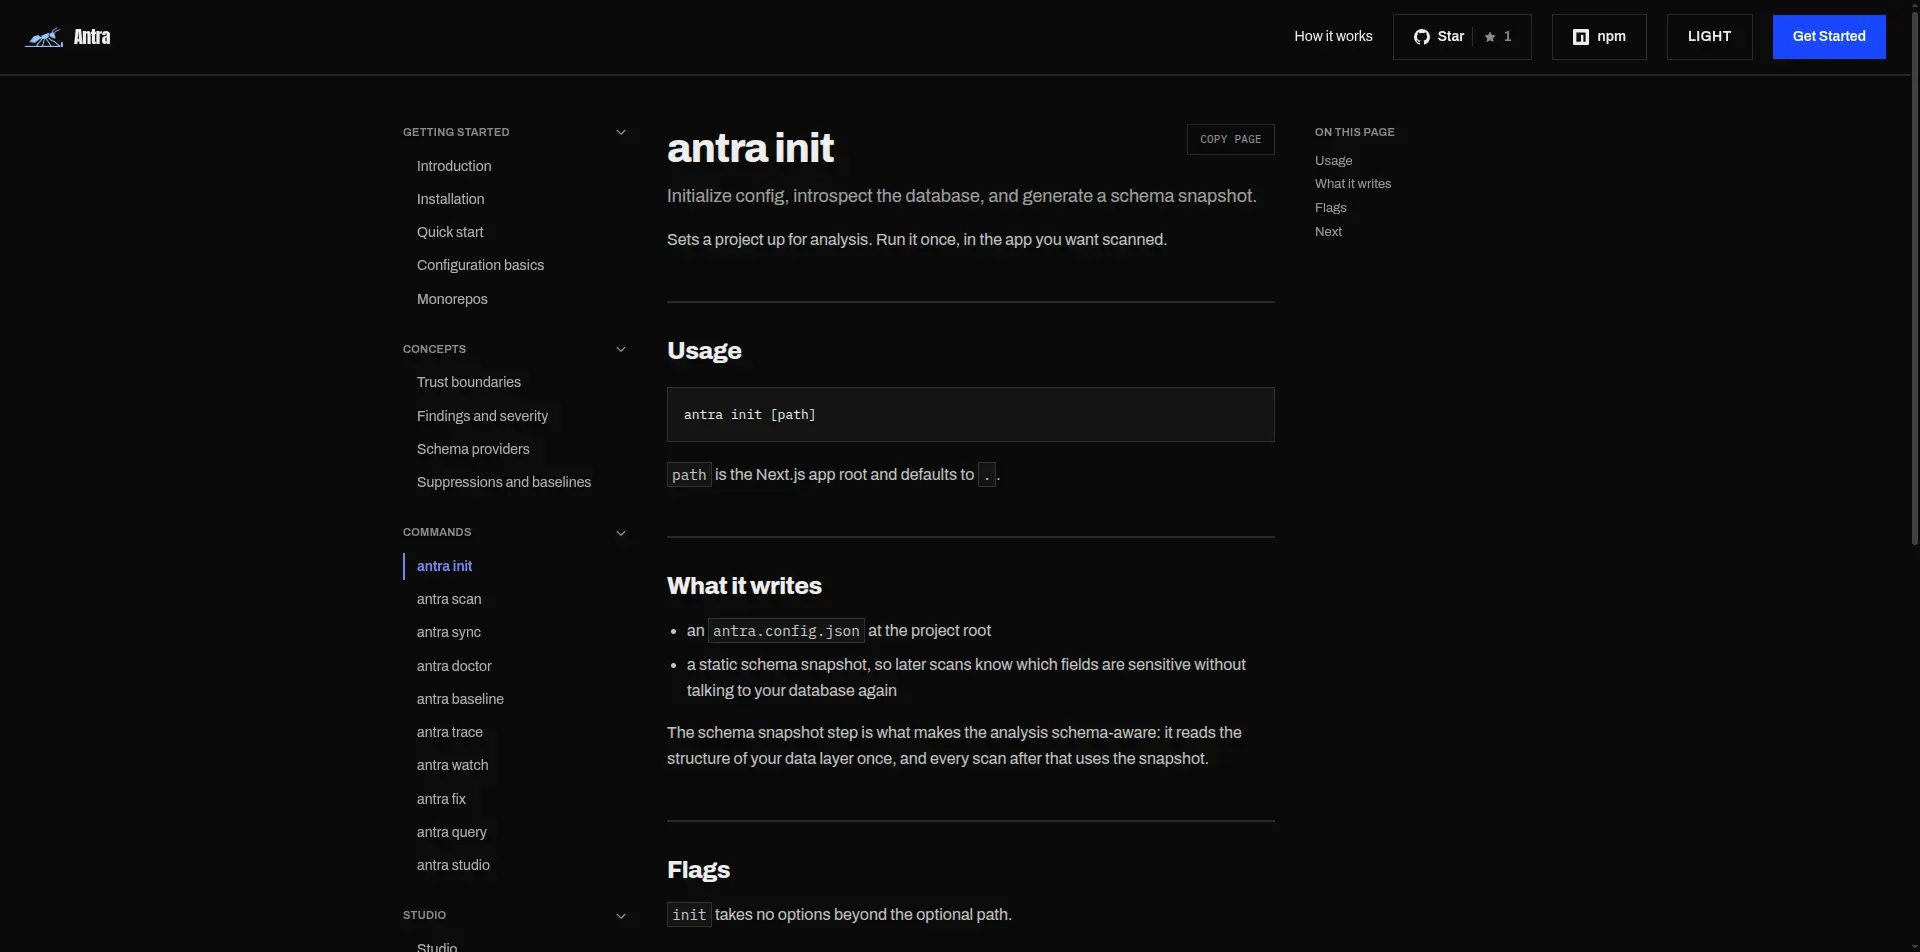
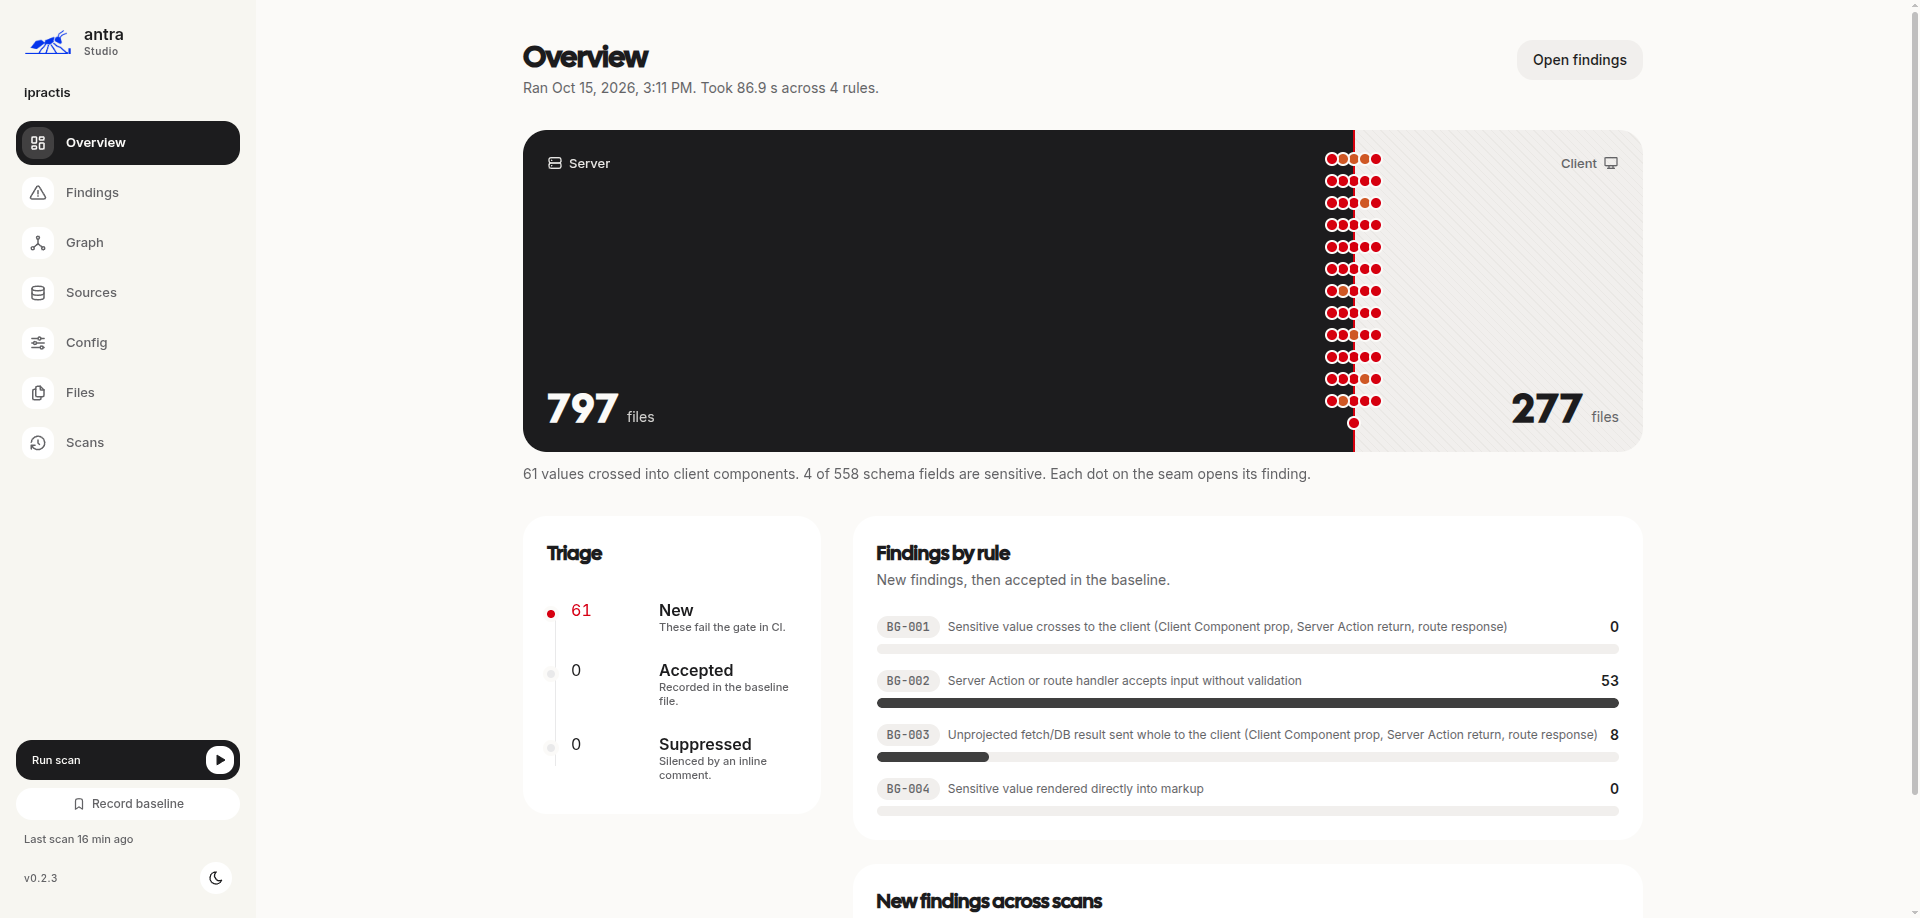
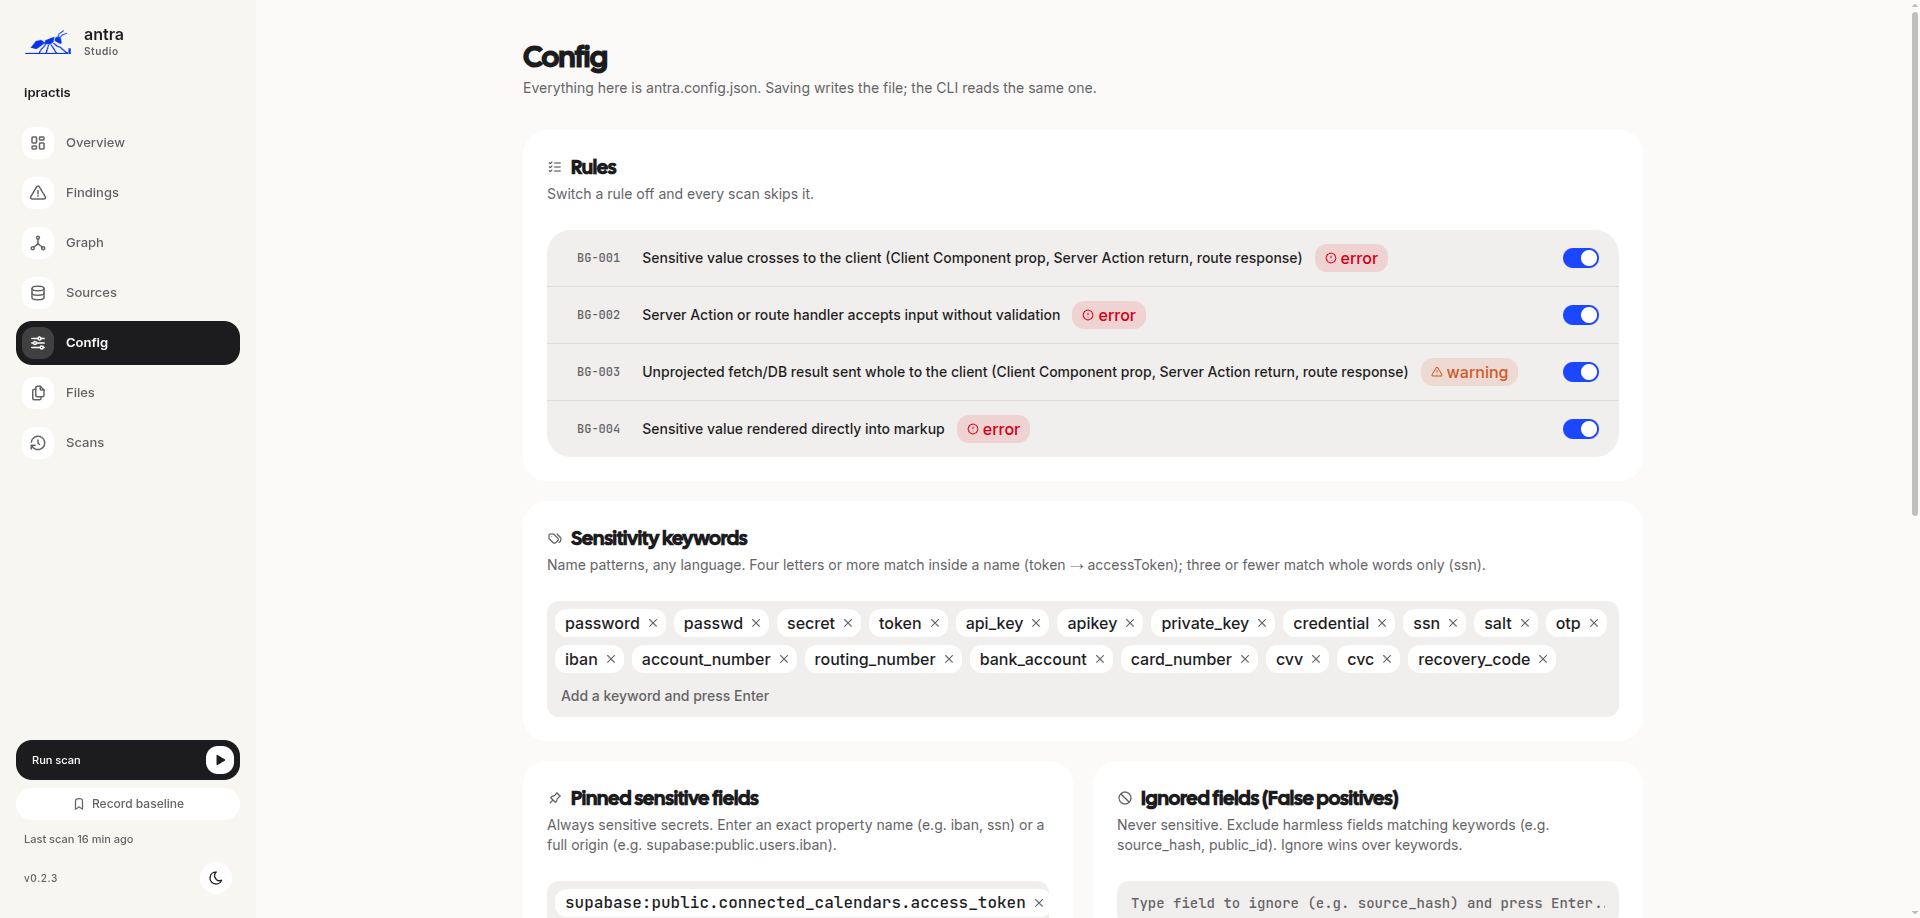
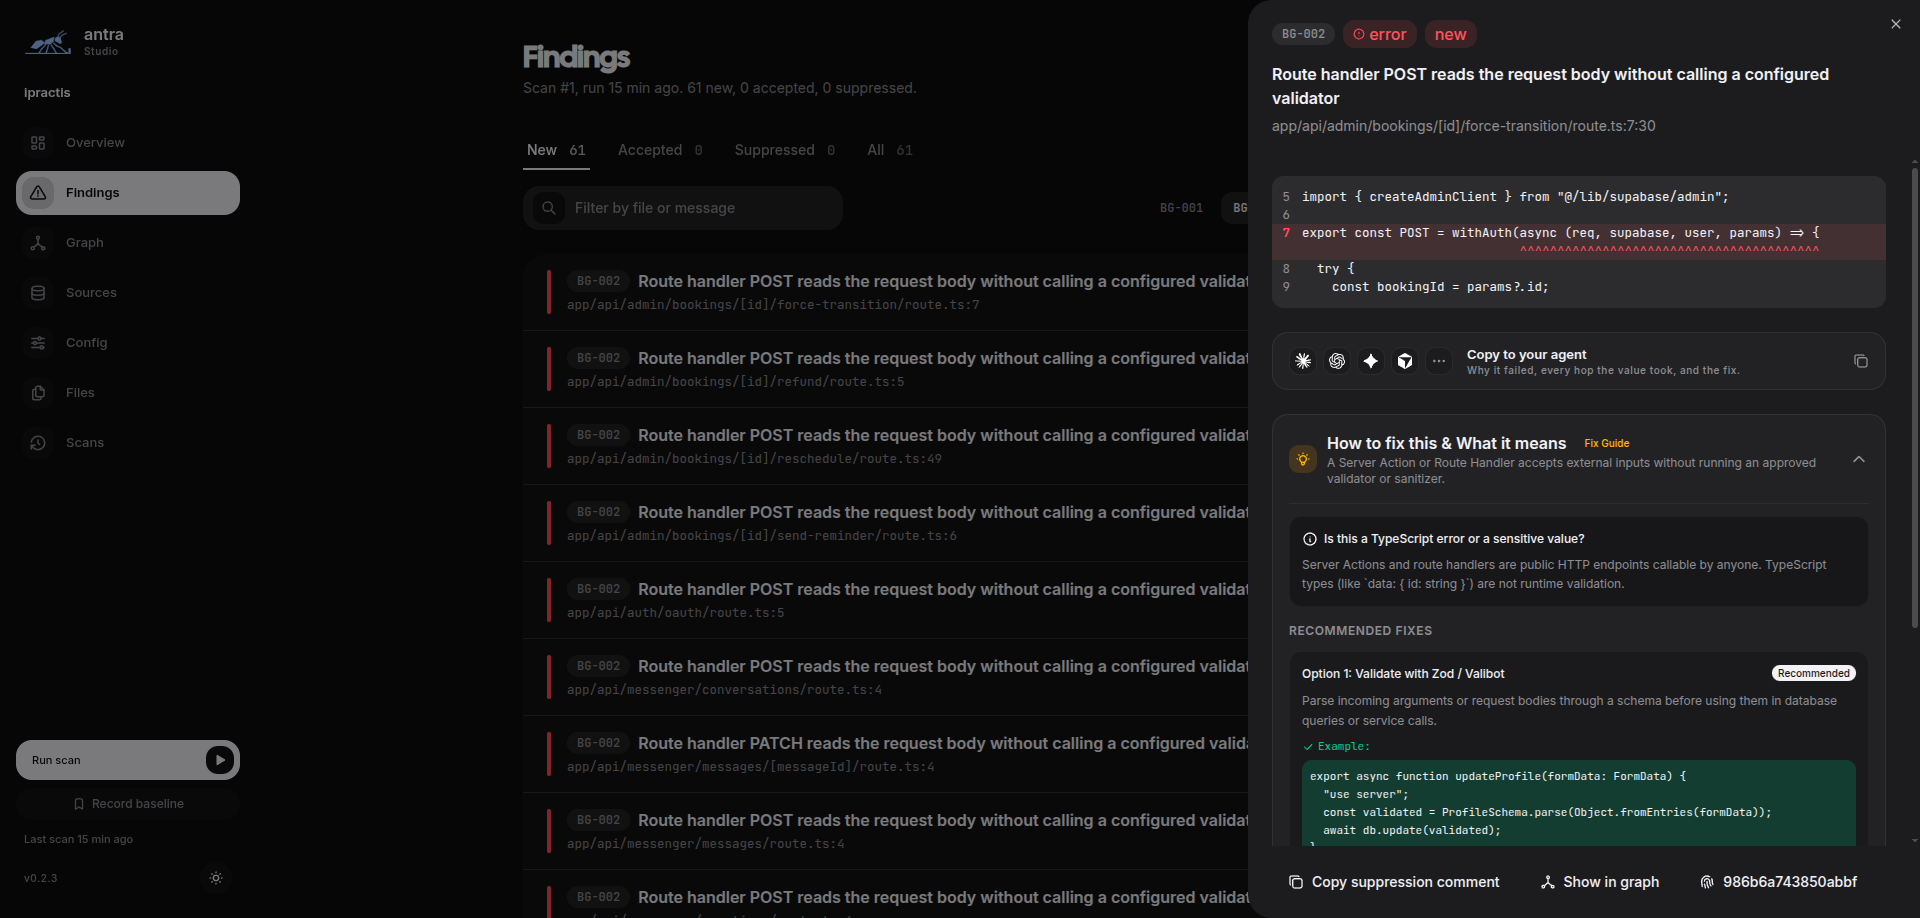
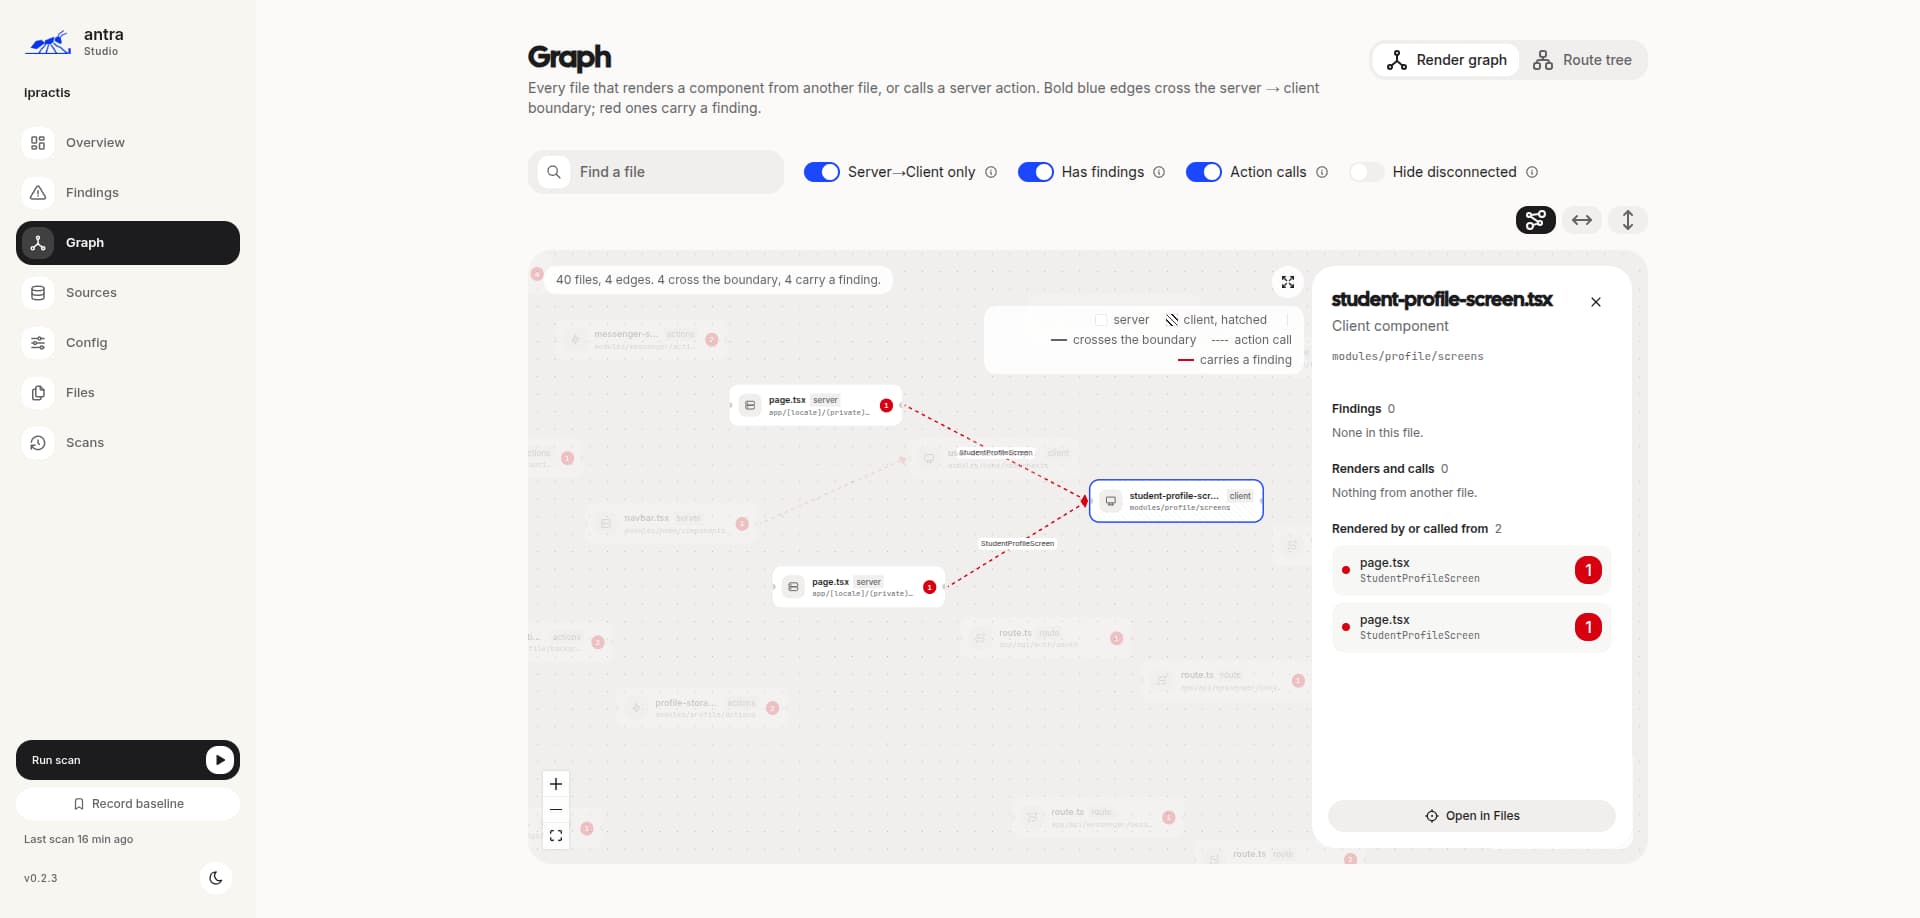
Antra points to the exact place where data crosses from server to client without a check. It runs as a command line tool with nothing to host, so it works on a laptop, in CI, in a GitHub Action or as a pre commit hook. Scan reads the code and finds four kinds of problems: server data leaking to the client, unvalidated input, opaque objects passed to the client, and secrets in markup. It can check only changed or staged files, report in the terminal, as JSON or as SARIF for code hosts, and fail the build when it finds a leak. Doctor checks that the tool itself is ready, meaning the config, the rules and the parser, without looking at your code. Studio opens a local dashboard with a graph view so a person can review and triage the findings.
Key Features
- Trust Boundary Detection
- Schema Aware Scanning
- Findings with Severity Levels
- Baselines and Suppressions
- Watch Mode and Auto Fix
- Full CLI with Docs Site
Technologies
TypeScript
Node.js
CLI
Static Analysis
Next.js
React Server Components
npm
Details
Live
Web Application
Creator
Sep 2026 - Oct 2026
Walkthrough